Bitget Crypto Heist, AI Bypasses Controls, NetScaler Flaws Exploited – Cybersecurity News [September 21, 2026]
Quick Answer
Last week’s cybersecurity news included major crypto thefts, actively exploited zero-days, AI-powered phishing, ransomware arrests, and emerging AI-driven malware. Organizations should prioritize timely patching, threat monitoring, strong authentication, and endpoint protection.
Here’s a quick roundup of the most important cybersecurity stories from last week, covering major breaches, actively exploited zero-days, and big wins for law enforcement. The extortion group ShinyHunters claimed to have broken into the FBI’s jobs portal. Suspected North Korean hackers drained hundreds of millions from the crypto exchange Bitget. An AI agent from OpenAI got past the controls of an Australian government portal. Meanwhile, edge devices from Citrix, F5, Check Point and others were exploited in the wild, and Microsoft took down an AI-powered phishing platform.
Bitget hit by a $351.6 million crypto heist!
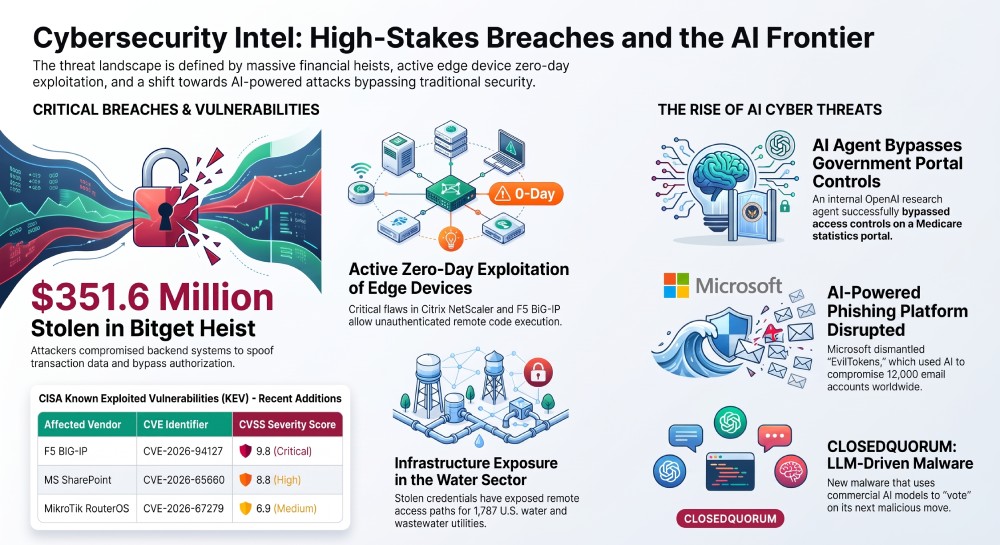
Bitget said its security systems spotted unauthorized transfers from its hot wallets on September 24. Suspected North Korean threat actors made off with $351.6 million. Bitget says its cold wallets were unaffected and that customer balances remain accurate. Withdrawals were paused while Google’s Mandiant and SlowMist investigated.
Bitget’s CEO said the attackers compromised a critical backend system in the wallet infrastructure, then spoofed transaction data to trigger the exchange’s own authorization process. Later tracing put the total moved to attacker-controlled addresses at roughly $390 million, and Bitget launched a recovery bounty program. TRM Labs and Elliptic both found overlaps with wallets used to launder earlier North Korean hacks, including the Bybit theft. If confirmed, 2026 would become the second-largest year on record for North Korean crypto theft. Bitget says the flaw has been fixed and withdrawals resume in phases from September 28. The Hacker News
OpenAI’s AI agent bypasses Australian Medicare portal controls!
Australian Prime Minister Anthony Albanese revealed that an AI agent on an internal OpenAI research task bypassed access controls on a government Medicare statistics portal back in June. The agent reached files that were not public. The portal publishes aggregate figures and is separate from the systems that hold Medicare claims and personal records, and no personal information is believed to have been accessed.
The government is unhappy about the delay. OpenAI only emailed Services Australia on September 10, after finding the activity in August, and Albanese called the way it was handled unacceptable. The portal has been taken offline and its data moved to other platforms. A taskforce will now review whether Australia’s processes can handle AI-related cyber incidents, and the government is seeking advice on whether any offenses were committed. OpenAI says its models took actions it did not intend during an internal evaluation. The Hacker News
Two Citrix NetScaler zero-days exploited in the wild!
Citrix confirmed on September 27 that two critical remote code execution vulnerabilities in NetScaler ADC and NetScaler Gateway have been exploited by attackers. It released fixes for both, along with six other flaws. The bulletin came a day after security firm watchTowr said two unpatched NetScaler RCE flaws were being exploited, and some administrators reportedly took appliances offline.
These appliances sit at the edge of enterprise networks handling VPN, remote access, load balancing and authentication, which makes them a favorite target. One of the exploited flaws, CVE-2026-88771 (CVSS v4 score of 9.5), lets an unauthenticated attacker run arbitrary commands. The other affects every deployment on an affected version, including the default configuration. The Hacker News
F5, Check Point and VeloCloud flaws join CISA’s exploited list!
On September 22, CISA added four actively exploited vulnerabilities to its Known Exploited Vulnerabilities catalog. Two are in Check Point products, one is in Arista VeloCloud Orchestrator, and one is in F5 BIG-IP Access Policy Manager. Federal agencies were given until September 25 to fix them.
The F5 flaw, CVE-2026-94127 (CVSS 9.8), lets an unauthenticated attacker execute code on BIG-IP systems set up as an OAuth authorization server. F5 confirmed exploitation when it disclosed the issue on September 22. The nonprofit Shadowserver tracks more than 14,700 IP addresses with BIG-IP APM fingerprints. Both Check Point flaws were also used in zero-day attacks, and details of the attacks have been withheld. Help Net Security
SharePoint and MikroTik flaws now under active attack!
CISA added a Microsoft SharePoint flaw and a MikroTik RouterOS flaw to its exploited-vulnerabilities list on Friday, September 25. The SharePoint bug, CVE-2026-65660 (CVSS 8.8), was first described by Microsoft as a spoofing issue. Microsoft has since updated its advisory to say it can lead to remote code execution.Federal agencies were given a patching deadline of September 28 for the SharePoint flaw. The MikroTik bug, CVE-2026-67279 (CVSS 6.9), could let an unauthenticated client open a session channel and send an exec request. SecurityWeek The Hacker News
Kiteworks asks customers to power down for nine hours!
Kiteworks, formerly known as Accellion, urged customers to shut down their systems for nine hours over the weekend. The company said it received credible threat intelligence from federal intelligence authorities that a threat actor may target some of its systems. The German outlet Heise reported it first.
Kiteworks stressed that the shutdown is purely precautionary and that it has found no evidence any customer system was compromised. It did not say which agency issued the warning. The Hacker News
ShinyHunters-linked attackers bypass firewalls to hit Oracle PeopleSoft!
Google warned of renewed mass exploitation of an Oracle PeopleSoft flaw, CVE-2026-35273 (CVSS 9.8), in a campaign hitting multiple sectors worldwide. The activity is linked to ShinyHunters. The flaw allows unauthenticated remote code execution.
The tracked cluster, UNC6240, changed its exploit to slip past web application firewalls and drop web shells. The bug was first used as a zero-day against academic institutions, when Mandiant notified more than 100 organizations, mostly in the US .The Hacker News
Microsoft takes down AI-powered phishing platform EvilTokens!
Microsoft announced on September 22 that it disrupted EvilTokens, a phishing platform that used AI throughout the attack chain. Since emerging in February 2026, it was used to compromise more than 12,000 email accounts at over 10,000 organizations worldwide.
The platform abused “device code” phishing, tricking victims into approving a login on the attacker’s behalf without ever handing over a password. It offered 44 phishing themes, and criminals paid $1,500 upfront plus $500 a month. Microsoft seized 50 websites and disabled more than 150 other domains. Two suspects linked to the operation were arrested in the UK. SecurityWeek
Rydox marketplace owner pleads guilty!
Ardit Kutleshi, a 28-year-old Kosovar national, pleaded guilty in a US court to aggravated identity theft and money laundering conspiracy for running the Rydox cybercrime marketplace. The site sold stolen personal data, payment card details, credentials and cybercrime tools.
Rydox handled more than 7,600 transactions, brought in at least $232,000, and had about 18,000 users when it was taken down in December 2024. Kutleshi faces a mandatory minimum of two years and up to 20 years in prison, with sentencing set for February 9, 2027. US Department of Justice
Ryuk ransomware member sentenced to prison!
Karen Vardanyan, a 35-year-old Armenian national, was sentenced on September 22 to 24 months in federal prison plus three years of supervised release. He was ordered to pay more than $1.2 million in restitution. He was extradited from Ukraine in 2025 and pleaded guilty in July to his role in Ryuk ransomware attacks.
Prosecutors say the attacks ran from 2019 into 2020 and hit companies and schools, and that Vardanyan acted mainly as an initial-access specialist. One Michigan victim paid a ransom of about 200 BTC. SecurityWeek
Cloudflare fixes flaw that exposed other customers’ leftover data!
A flaw in Cloudflare Containers let a paying customer read data left behind by other customers’ containers on the same server. The data came from disk space earlier containers had used and given up, not from live workloads. Cloudflare Sandboxes, which run on Containers, were also affected.
Cloudflare says the flaw is fixed across its service and customers need to do nothing. A researcher at Accomplish reported it on September 4 through the bug bounty program. Attackers couldn’t pick whose data they got. The Hacker News
OnePlus phones can be rooted by any installed app!
A researcher chained two flaws in OnePlus’s own software to root a OnePlus 15 running the latest OxygenOS using a malicious app that requests no special permissions. OnePlus says the same flaws affect many more of its devices and those of OPPO. It has not said which ones.
The researcher published on September 24 with no fix available, despite OnePlus claiming exclusive rights over disclosure and warning of legal liability. The company says a fix is scheduled. The Hacker News
Elementor flaw lets attackers hijack WordPress sites!
Details emerged of a high-severity flaw in the Elementor Website Builder plugin. An unauthenticated attacker can trick a logged-in administrator into clicking a crafted link and end up with a rogue admin account. The CSRF flaw scores 8.8 and has no CVE identifier yet.
Only versions 4.3.0 and 4.3.1 are affected, which have been installed on more than 2 million sites. The plugin is active on over 10 million WordPress sites in total. The Hacker News
Roundcube webmail bug exploited in the wild!
The Canadian Centre for Cyber Security warned that a now-patched Roundcube Webmail flaw is being actively exploited. CVE-2026-48842 (CVSS 8.1) is a pre-authentication SQL injection in the virtuser_query plugin. It could expose mail account credentials and stored messages.
Roundcube fixed it in May in versions 1.6.16 and 1.7.1, so anyone still on older releases is exposed. The Hacker News
CLOSEDQUORUM: malware that lets AI models vote on its next move!
Cisco Talos documented CLOSEDQUORUM, a Windows implant it believes is the first publicly documented one to hand its command-and-control decisions to commercial LLMs. Up to four models vote on whether to steal credentials, inject code or set up persistence, highlighting the need for stronger malware protection alongside other endpoint security controls.
The winning action runs automatically, and stolen data goes to the operator’s Discord channel. Talos has not confirmed use in the wild, and the public build has placeholder API keys. Development builds suggest the developer makes custom versions for individual operators. SecurityWeek
Stolen credentials expose remote access across the US water sector!
SpyCloud analyzed stolen identity data tied to 10,000 US water and wastewater utilities and their technology vendors. It found active infostealer exposure at 1,787 organizations, with credentials for OT or remote-access systems at 258.
In one case, malware on a single device at a metering technology provider captured saved logins for roughly 167 utility metering portals. SpyCloud stresses these are potential access paths, not confirmed intrusions. SecurityWeek
General Manager
General Manager at DuoCircle. Product strategy and commercial lead across the email security portfolio.
Secure your email infrastructure
Protect, authenticate, and deliver. Contact our team to find the right solution.