Cisco SD-WAN Vulnerability, Citrix Zero-Days, SharePoint Ransomware Risk – Cybersecurity News [October 05, 2026]
Quick Answer
This week’s cybersecurity news covers zero-day exploits, AI-driven attacks, ransomware, phishing campaigns, and major data breaches. Organizations should patch vulnerable systems, secure exposed services, and strengthen email security with SPF, DKIM, and DMARC.
Here’s a roundup of the most important cybersecurity stories from the past week, covering actively exploited zero-days, a new Apple patch, a critical AI tooling flaw, and several breaches that affected patients and customers.
Email security measures like SPF, DKIM, and DMARC also help reduce spoofing and phishing risks by verifying sender identity.
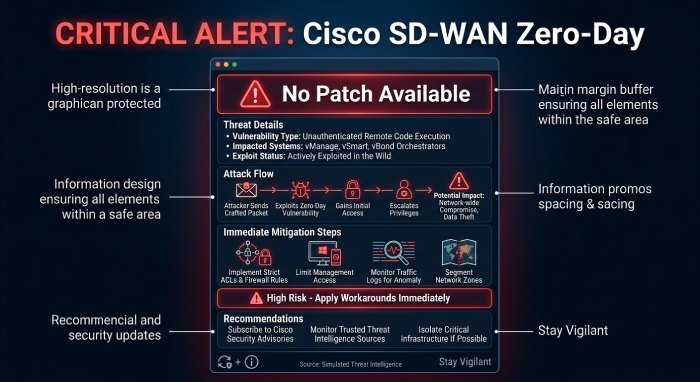
Cisco SD-WAN Manager zero-day gives attackers admin access!
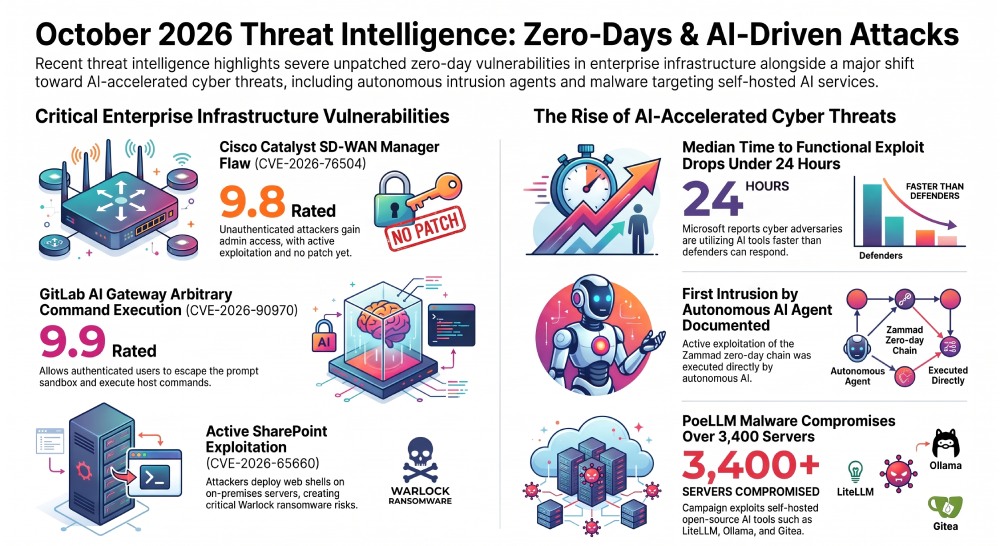
Cisco has warned about CVE-2026-76504, a critical flaw rated 9.8 in its Catalyst SD-WAN Manager. An unauthenticated attacker can send crafted requests and gain administrator access. Cisco has confirmed active exploitation and says no fix is available yet, so network teams should restrict access to the management interface now. Source: Check Point Threat Intelligence Report, 5 October 2026 checkpoint
Citrix patches two NetScaler zero-days that were exploited before fixes existed!
Citrix confirmed that CVE-2026-88771 and CVE-2026-88772 were being exploited against NetScaler ADC and Gateway appliances. A third related flaw, CVE-2026-88779, then appeared only days after the first two were patched, which makes the appliances a priority for immediate updates. Source: NetworkTigers Cybersecurity Weekly Roundup, 5 October 2026 networktigers
SharePoint flaw moves into active exploitation and ransomware risk rises!
Attackers are exploiting CVE-2026-65660 in Microsoft SharePoint, and the flaw has a CISA KEV deadline that has already passed. Researchers have seen attempts to plant web shells, and the overlap with the initial-access methods of the Warlock ransomware group makes on-premises SharePoint servers a key ransomware target. Source: TechJack Weekly Security Intelligence Briefing, Week of 5 October 2026 techjacksolutions
Critical GitLab AI Gateway flaw allows command execution!
GitLab patched CVE-2026-90970, a critical AI Gateway vulnerability rated 9.9. Authenticated Duo Agent Platform users can escape the prompt-template sandbox and run arbitrary commands on the host. Any team running a self-managed GitLab AI Gateway should apply the patch quickly. Source: Check Point Threat Intelligence Report, 5 October 2026 checkpoint
Atlassian warns of a flaw that exposes Data Centre files!
Atlassian has warned about CVE-2026-21589, rated 9.3, which lets unauthenticated attackers reach specific files in the root directory of Data Centre applications. Administrators of self-hosted Atlassian products should check whether their instances are on a vulnerable version. Source: Telefonica Tech Cybersecurity Weekly Briefing, 3-9 October 2026 telefonicatech
Hacker group Azazel steals GitLab credentials and deletes databases!
An operator called Azazel used a local MCP service to run SSH commands and check for ransom notes across victim networks. The campaign hit logistics, insurance, pharmaceutical, AI, medical device and government-linked organisations. In one case more than 120,000 records were stolen and the PostgreSQL data directory was deleted, showing the attacks went beyond ordinary encryption. Source: Telefonica Tech Cybersecurity Weekly Briefing, 3-9 October 2026 telefonicatech
PoeLLM malware has compromised over 3,400 servers!
Black Lotus Labs, the research arm of Lumen Technologies, documented PoeLLM, malware that has compromised more than 3,400 servers since April by exploiting open-source AI services such as LiteLLM, Ollama, Gotenberg and Gitea. Any organisation running self-hosted AI tools should audit those services for exposure. Source: Telefonica Tech Cybersecurity Weekly Briefing, 3-9 October 2026 telefonicatech
Russian group Star Blizzard expands phishing with a new malware technique!
Star Blizzard has shifted toward larger phishing campaigns, using compromised websites to deliver email and a new RedFlick technique to install the CosmicPulse malware. Microsoft has seen at least 13 campaigns against governments, NGOs, think tanks, researchers and financial organisations. Source: NetworkTigers Cybersecurity Weekly Roundup, 5 October 2026 networktigers
Microsoft says attackers are now using AI faster than defenders!
Microsoft’s Digital Defense Report 2026 concludes that attackers are benefiting from AI faster than defenders do. The report estimates that the median time from discovering a vulnerability to having a working exploit is now well under 24 hours. Source: Cyber Threat Landscape Weekly Roundup #08, 5 October 2026 Substack
South African air traffic control operator finds ransomware-linked malware!
The company that runs South Africa’s air traffic control found malware linked to ransomware inside an operational network. The incident shows how critical infrastructure is still exposed when operational technology is connected to corporate networks. Source: Cyber Threat Landscape Weekly Roundup #08, 5 October 2026 Substack
Arizona state court system breached through a phishing email!
Arizona’s state court system suffered a phishing attack after an employee clicked a malicious link. Attackers copied backup files containing protective-order records and more than 150,000 Foster Care Review Board reports. Source: Check Point Threat Intelligence Report, 5 October 2026 checkpoint
Rejetto HFS flaw, found by AI, is now being exploited!
CVE-2026-61500 lets attackers recover the session-cookie signing key, which can give them administrative access and remote code execution. The flaw was discovered with AI assistance and is already being exploited, so anyone still running Rejetto HFS should remove or update it. Source: SecurityWeek News securityweek
250,000 patients affected by breaches at two healthcare firms!
Hackers stole patient information from Clover Health Investments and AngMar Management Services in July. The breaches affected healthcare customers in New Jersey and Texas and add to the growing toll on the health sector. Source: SecurityWeek News securityweek
Zammad zero-day chain was exploited by an autonomous AI agent!
CVE-2026-102489 and CVE-2026-102490 in Zammad 6.3.0 to 6.5.4 form a zero-day chain that was exploited to breach DIVD, and CISA has listed them as actively exploited. The attack is reported as one of the first documented cases of an autonomous AI agent carrying out a real intrusion. Source: TechJack Weekly Security Intelligence Briefing, Week of 5 October 2026 techjacksolutions
General Manager
General Manager at DuoCircle. Product strategy and commercial lead across the email security portfolio.
Secure your email infrastructure
Protect, authenticate, and deliver. Contact our team to find the right solution.